Security
Every company sealed off. Every change on the record.
Each company's books live in their own isolated store, bank access is read-only, and every change can be traced and undone. Here is how your books are stored and who can change them.
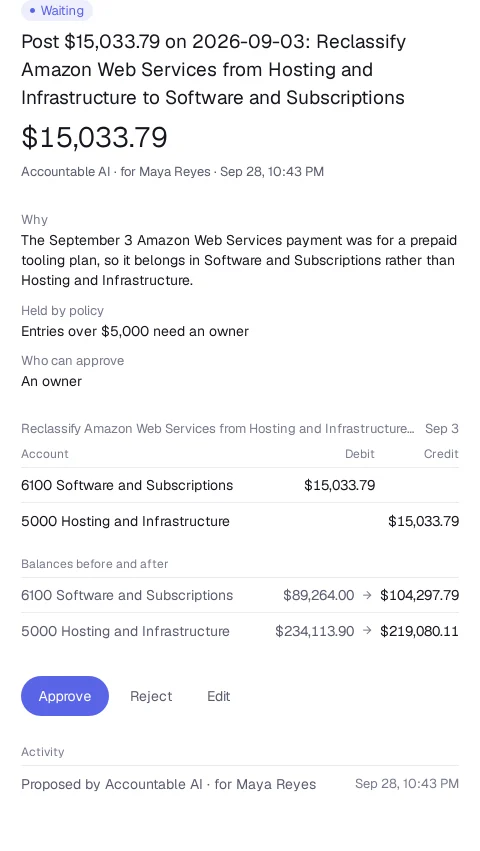
A big change waits for a person
This entry was proposed by Accountable AI. It shows who proposed it and why, the rule that held it, who can approve it, and every balance before and after. Once posted, it can be undone.
Each company's books live in their own isolated store
Every company gets its own Durable Object on Cloudflare, with its own SQLite database for the ledger. Before any request reaches a company's books, we check that you are a member of that company. You see only the companies you have access to.
- One store per company, so one company's data never sits in another company's database.
- A membership check runs before every request is routed to a company.
- The web app, the in-app AI and outside agents all write through the same checked path. There is no second way in.
Every change is logged, and every change can be undone
Every change names who made it: a person, Accountable AI, or an outside agent and the person whose connection it used. The log records the time, the reason, and the values before and after.
- Posted entries are never edited or deleted. Undo writes a reversing entry and links the two.
- Every entry balances to the cent before it posts.
- Each preview applies once, and every write carries a unique key, so a retry never posts twice.
- A closed month stays locked. Reopening it needs the right role and a logged reason.
- A whole migration can be undone for 30 days.
Agents cannot move money or manage users
The commands to move money or change users and billing are not in the agent tool list at all. Agents can only work on the books, and risky changes wait for a person.
- Entries of $500 or more, changes to closed months, deletions, chart of accounts changes and reopening a month wait for approval.
- An agent can never approve its own change. A person approves in the app, by email or in Slack.
- Every agent write shows the full change before it applies.
Bank access is read-only, and credentials are encrypted
Accountable reads your bank, card and payment data. It never moves money. Bank credentials and sign-in tokens for your connected sources are encrypted with a secret key held in Cloudflare Workers.
Your books are yours to export, on every plan
Export is never behind a paywall. Neither is import or your accountant's seat.
- Export any time as PDF, Excel or CSV, or as a one-click financial package.
- If your paid plan ends, your books fall back to free, read-only access.
- We never delete a company's books because a plan ended.
Your data lives on Cloudflare
Accountable runs on Cloudflare Workers. Each company's ledger lives in its own Durable Object.
- D1 holds shared records: users, workspaces, companies, memberships and roles, billing and source connections.
- R2 holds documents such as statements, receipts, exports and migration files, stored by company.
- AI requests go through the Vercel AI Gateway.
- Payments run through Stripe Checkout and the Stripe Customer Portal.
- A SOC 2 Type I audit is planned, followed by Type II.
Sign-in uses BetterAuth, with two-factor authentication
You sign in with Google or an email code, and you can turn on two-factor authentication. Roles decide what each person can do.
- Roles: owner, admin, member, accountant and viewer. The accountant seat is free.
- Outside agents such as Claude and ChatGPT connect through OAuth, with Accountable as the sign-in server.
Report a vulnerability, and we won't come after you for good-faith research
Email security@accountable.im. Our Vulnerability Disclosure Policy at /legal/vulnerability-disclosure says what is in scope, how to test safely, and our safe harbor. We aim to reply within 3 business days.
- In scope: the app, the public API, the MCP server and OAuth, and the separation between companies.
- Test only on accounts and companies you create. Never touch a real company's books.
- Give us 90 days to fix an issue before you publish it.
- Our contact is also in /.well-known/security.txt.
Read the Vulnerability Disclosure Policy, the Data Processing Addendum, the list of subprocessors and our Privacy Policy. Security reports go to security@accountable.im.
Close your next month by the 1st.
Free for one company. 14 days of Pro with no card. Moving your books is free. No sales calls.